ISO 31000 Certification
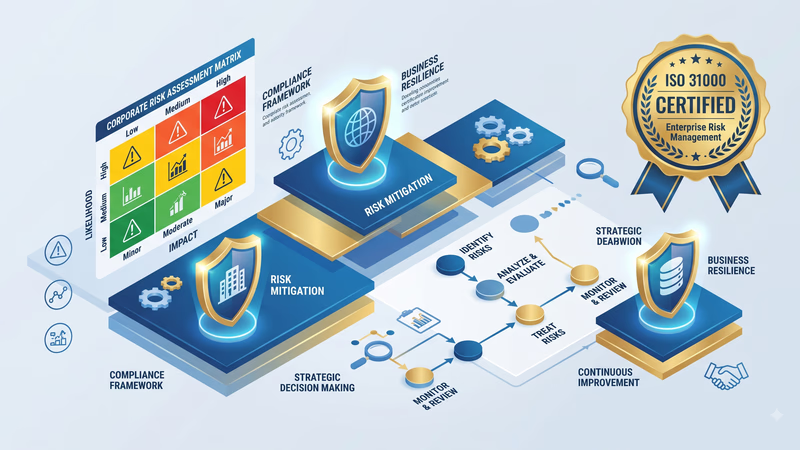
ISO 31000:2018 enables enterprises of all sizes—from growing manufacturing firms to BFSI companies and infrastructure developers—to embed risk management into core decision-making. Corporate buyers, investors, and public sector tender committees look for ISO 31000 compliance as definitive evidence of operational maturity and risk resilience.
What You Gain From This Certification
Here is how this certification helps your business grow and win more clients:
Establishes a comprehensive Enterprise Risk Management (ERM) framework across departments
Builds stakeholder, investor, and board confidence for major corporate transactions and public tenders
Verifiable Statement of Compliance / Attestation issued by recognized independent audit registrars
Reduces unexpected financial losses, regulatory fines, and operational supply chain downtime
Valid for 3 years, backed by proactive reminders and support for annual surveillance reviews
How Long Does It Take?
Clear, predictable completion timelines from initial document submission through audit review and certificate grant.
Timelines begin after document submission and depend on prompt review sign-offs and audit scheduling.
Documents Required
We keep documentation minimal and straightforward: basic business proof (GST, PAN, or MSME), signatory identification, and recent sale/purchase bills. We handle all technical manuals, SOP drafts, and filing paperwork for you.
Company Incorporation Certificate, GST, or MSME Udyam
PAN Card & Aadhaar of the Authorized Signatory
Copy of Recent Sale and Purchase Bills
Basic Overview of Products Manufactured or Services Provided
How We Get You Certified: Step-by-Step
Here is exactly what happens from the day you contact us to the day you get your certificate:
Context & Risk Scope Definition
We review your business operations, corporate goals, legal obligations, and internal risk appetite.
Risk Identification & Vulnerability Mapping
We identify operational, financial, technological, supply chain, and regulatory risks across departments.
Risk Assessment Matrix & Mitigation SOPs
We formulate risk likelihood and impact matrices, treatment action plans, and residual risk acceptance criteria.
Management Training & Mock Risk Audit
We train department heads on maintaining risk registers and conduct a mock review to resolve any procedural gaps.
Independent Assessment & Attestation Grant
We coordinate with the independent certification body for third-party assessment and deliver your Certificate of Compliance.
Who Needs This?
This certification is commonly needed by businesses in these industries:
Banking & Financial Services (BFSI)
Infrastructure & Energy Sector
Corporate Enterprises & Conglomerates
Supply Chain & Global Logistics
Why Businesses Choose Us
Here is what you can expect when you work with us:
Hands-on experience developing corporate risk frameworks for manufacturing, logistics, and BFSI sectors across India
Practical risk assessment tools designed for immediate operational use without bureaucratic bloat
Fixed, all-inclusive pricing covering risk registers, policy drafting, and registrar coordination
Continuous advisory support for annual risk reviews and corporate governance audits
Common Questions
Answers to the questions we hear most often about this certification:
The entire process for ISO 31000 Certification typically takes 3 to 15 Working Days from initial documentation drafting through verification and final issuance.
ISO 31000 is an international guidance standard. Organizations undergo an independent third-party assessment and receive an official Certificate of Compliance / Attestation of Conformity that serves as verifiable proof to clients, investors, and tender authorities.
ISO 9001 is a quality management standard that includes risk-based thinking for operational processes. ISO 31000 is a dedicated enterprise-wide framework covering financial, operational, strategic, legal, and market risks across the entire organization.
You only need basic business registration proofs (GST, PAN, or MSME Udyam), signatory KYC, recent sale/purchase bills, and a brief description of your business activities. We draft all required risk matrices, treatment plans, and governance registers for you.
Banking and financial services (BFSI), infrastructure and energy conglomerates, large logistics networks, and corporate manufacturers tendering for major public and private projects benefit significantly from ISO 31000.
Accredited attestations can be verified online through the issuing certification body's official verification portal using your unique certificate reference number.
Accredited certificates are issued under recognized international accreditation bodies (such as IAF member boards) and are generally required for government tenders, institutional clients, and global exports. Non-accredited certificates are verified through independent certification registrars, making them faster and cost-effective for commercial vendor onboarding and internal quality management. We help you choose the right option based on your buyer requirements.
We keep documentation minimal: basic business registration proof (GST, PAN, or MSME), signatory Aadhaar/PAN, and recent sale/purchase bills. Our consultants draft your entire quality manual, SOPs, and audit registers so you don't have to write paperwork from scratch.
Most ISO management certifications (including ISO 9001, 14001, 45001, and 27001) are completed in 3 to 15 working days once basic documentation is submitted and audit scheduling is finalized.
The cost depends on whether you require an accredited or non-accredited certificate, your team size, and facility locations. Contact us for a clear, all-inclusive quote upfront with no hidden fees.
Your certificate is valid for 3 years, but there is a short check-up audit every year to make sure you are still following the standards. We help you prepare for these annual surveillance audits too, so you never lose your certification.
Related Standards
Other certifications and compliance standards commonly required in your sector:
Guides & Resources
Read our plain-English guides to understand more about compliance and certification:
Available Locations
We support businesses with ISO 31000 Certification in these cities: